Multi-layer protection at the edge
keeps malicious requests away from your origin
Six layers: access lists, CC, bots, WAF, upload scanning and auto-ban. With Rules Update, vulnerability patches, emergency rules and the high-risk IP library sync hourly.
Six-layer protection system
Listed in the order in which a request is processed; the blocks of each layer are counted separately under Protection results on the security posture screen
Access lists and control
- IP and range allow/block lists, global or per site
- Allow or block by country, province or carrier
- Rules on UA, Referer and request method
CC protection
- Rate limits by IP or URL; challenge or block when exceeded
- JS and slider challenges
- Thresholds per site and per path
Bots and scanners
- Detects scanners such as nuclei, masscan and zgrab
- Detects spoofed UAs and headless browsers
- Search-engine crawlers are allowed automatically
WAF rule engine
- Based on OWASP CRS v4; built-in rules ship with each release
- Three protection levels, adjustable per site
- New rules only log for 3 days before blocking, to cut false positives
Upload scanning
- Dangerous file types are blocked directly
- Trojan / webshell signatures (Plus)
- ClamAV virus library on nodes with ≥ 4 GB RAM (Plus)
Auto-ban and high-risk IP library
- Repeat offenders are banned automatically and released on expiry
- High-risk IP library updated hourly (Rules Update)
- Banned IPs are stopped at the node when they return
Security posture screen: attack sources and block results in real time
Available with WAF Plus, with full-screen display and automatic refresh. Without it, Security Overview and Attack Logs remain available.
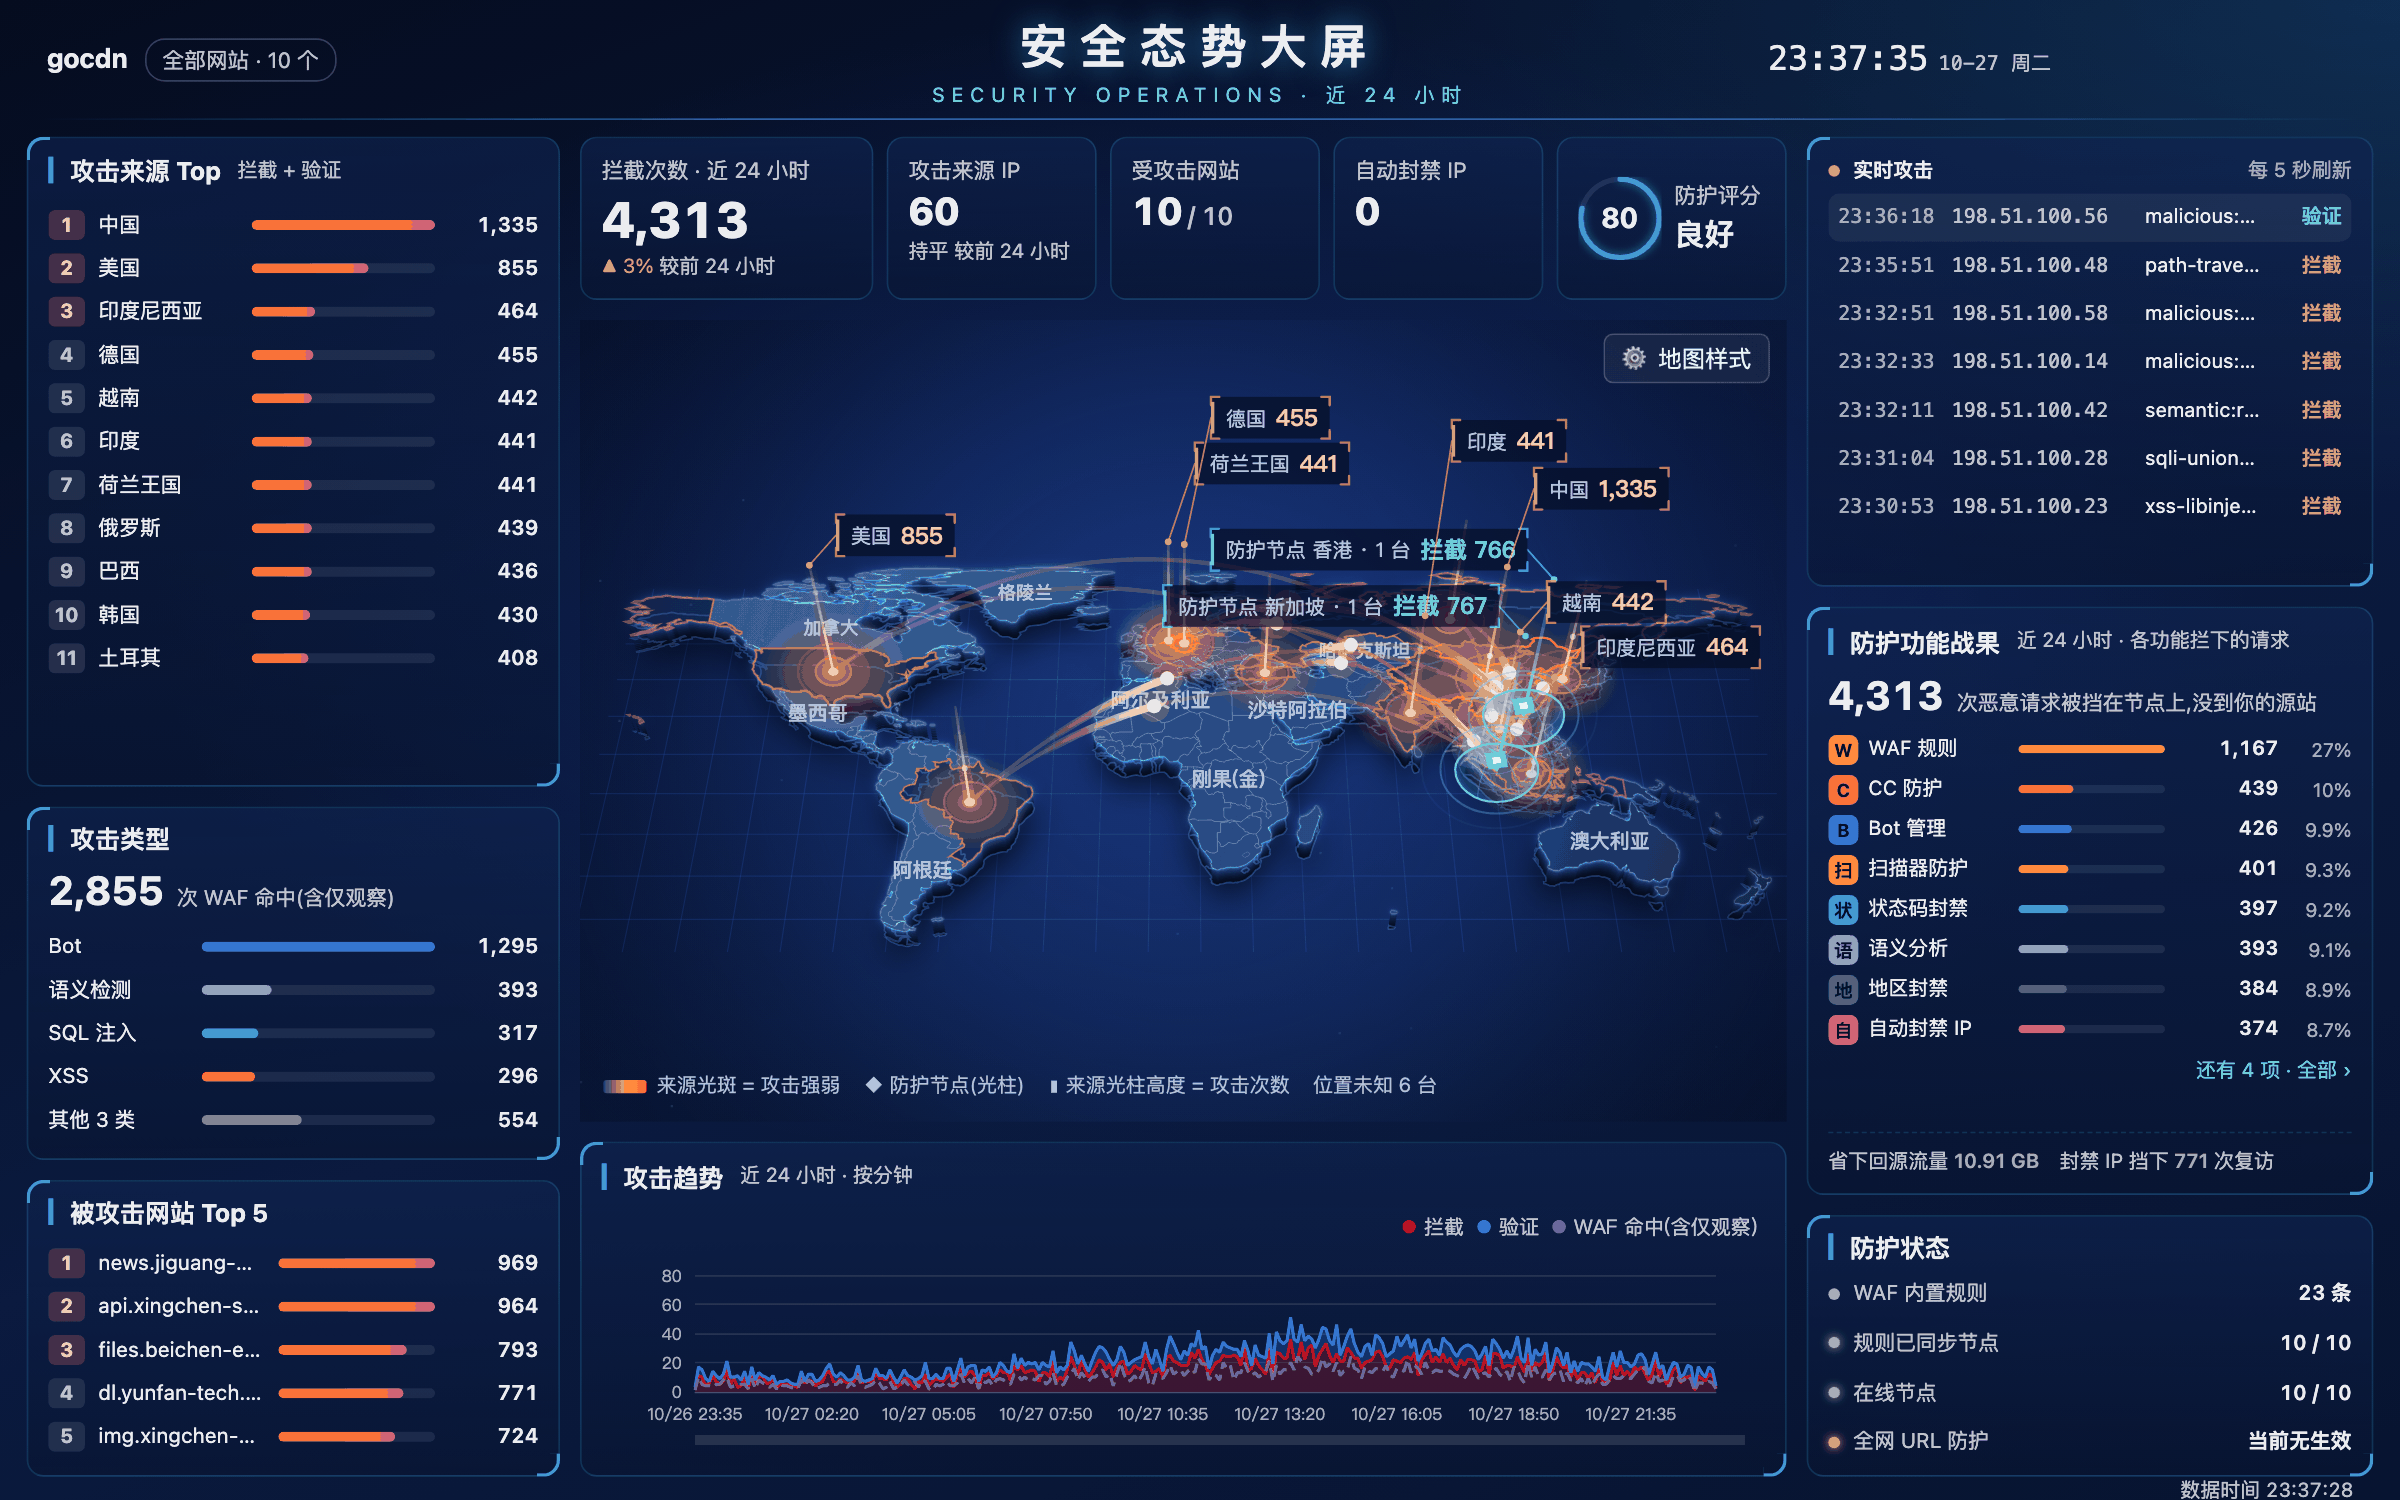
Attack map
Source countries and cities and the targeted edge node; bar height indicates the number of attacks
Live attacks
Refreshed every 5 seconds: time, source IP, target, matched rule, action
Protection results
Blocked requests and origin traffic saved, by protection feature (CC, WAF, auto-ban, region blocking and others)
Protection score
Scored from protection switches and rule sync status; each deduction links directly to the setting to correct
WAF rules
Rule pack: OWASP CRS v4 conversions + vulnerability patches; without Rules Update, the built-in 23 rules are used
High-risk IP library
Updated hourly · Rules Update
Attack event retention
Every block can be traced to its request and matched rule
Protection features counted separately
Blocked requests are counted per feature under Protection results on the security posture screen
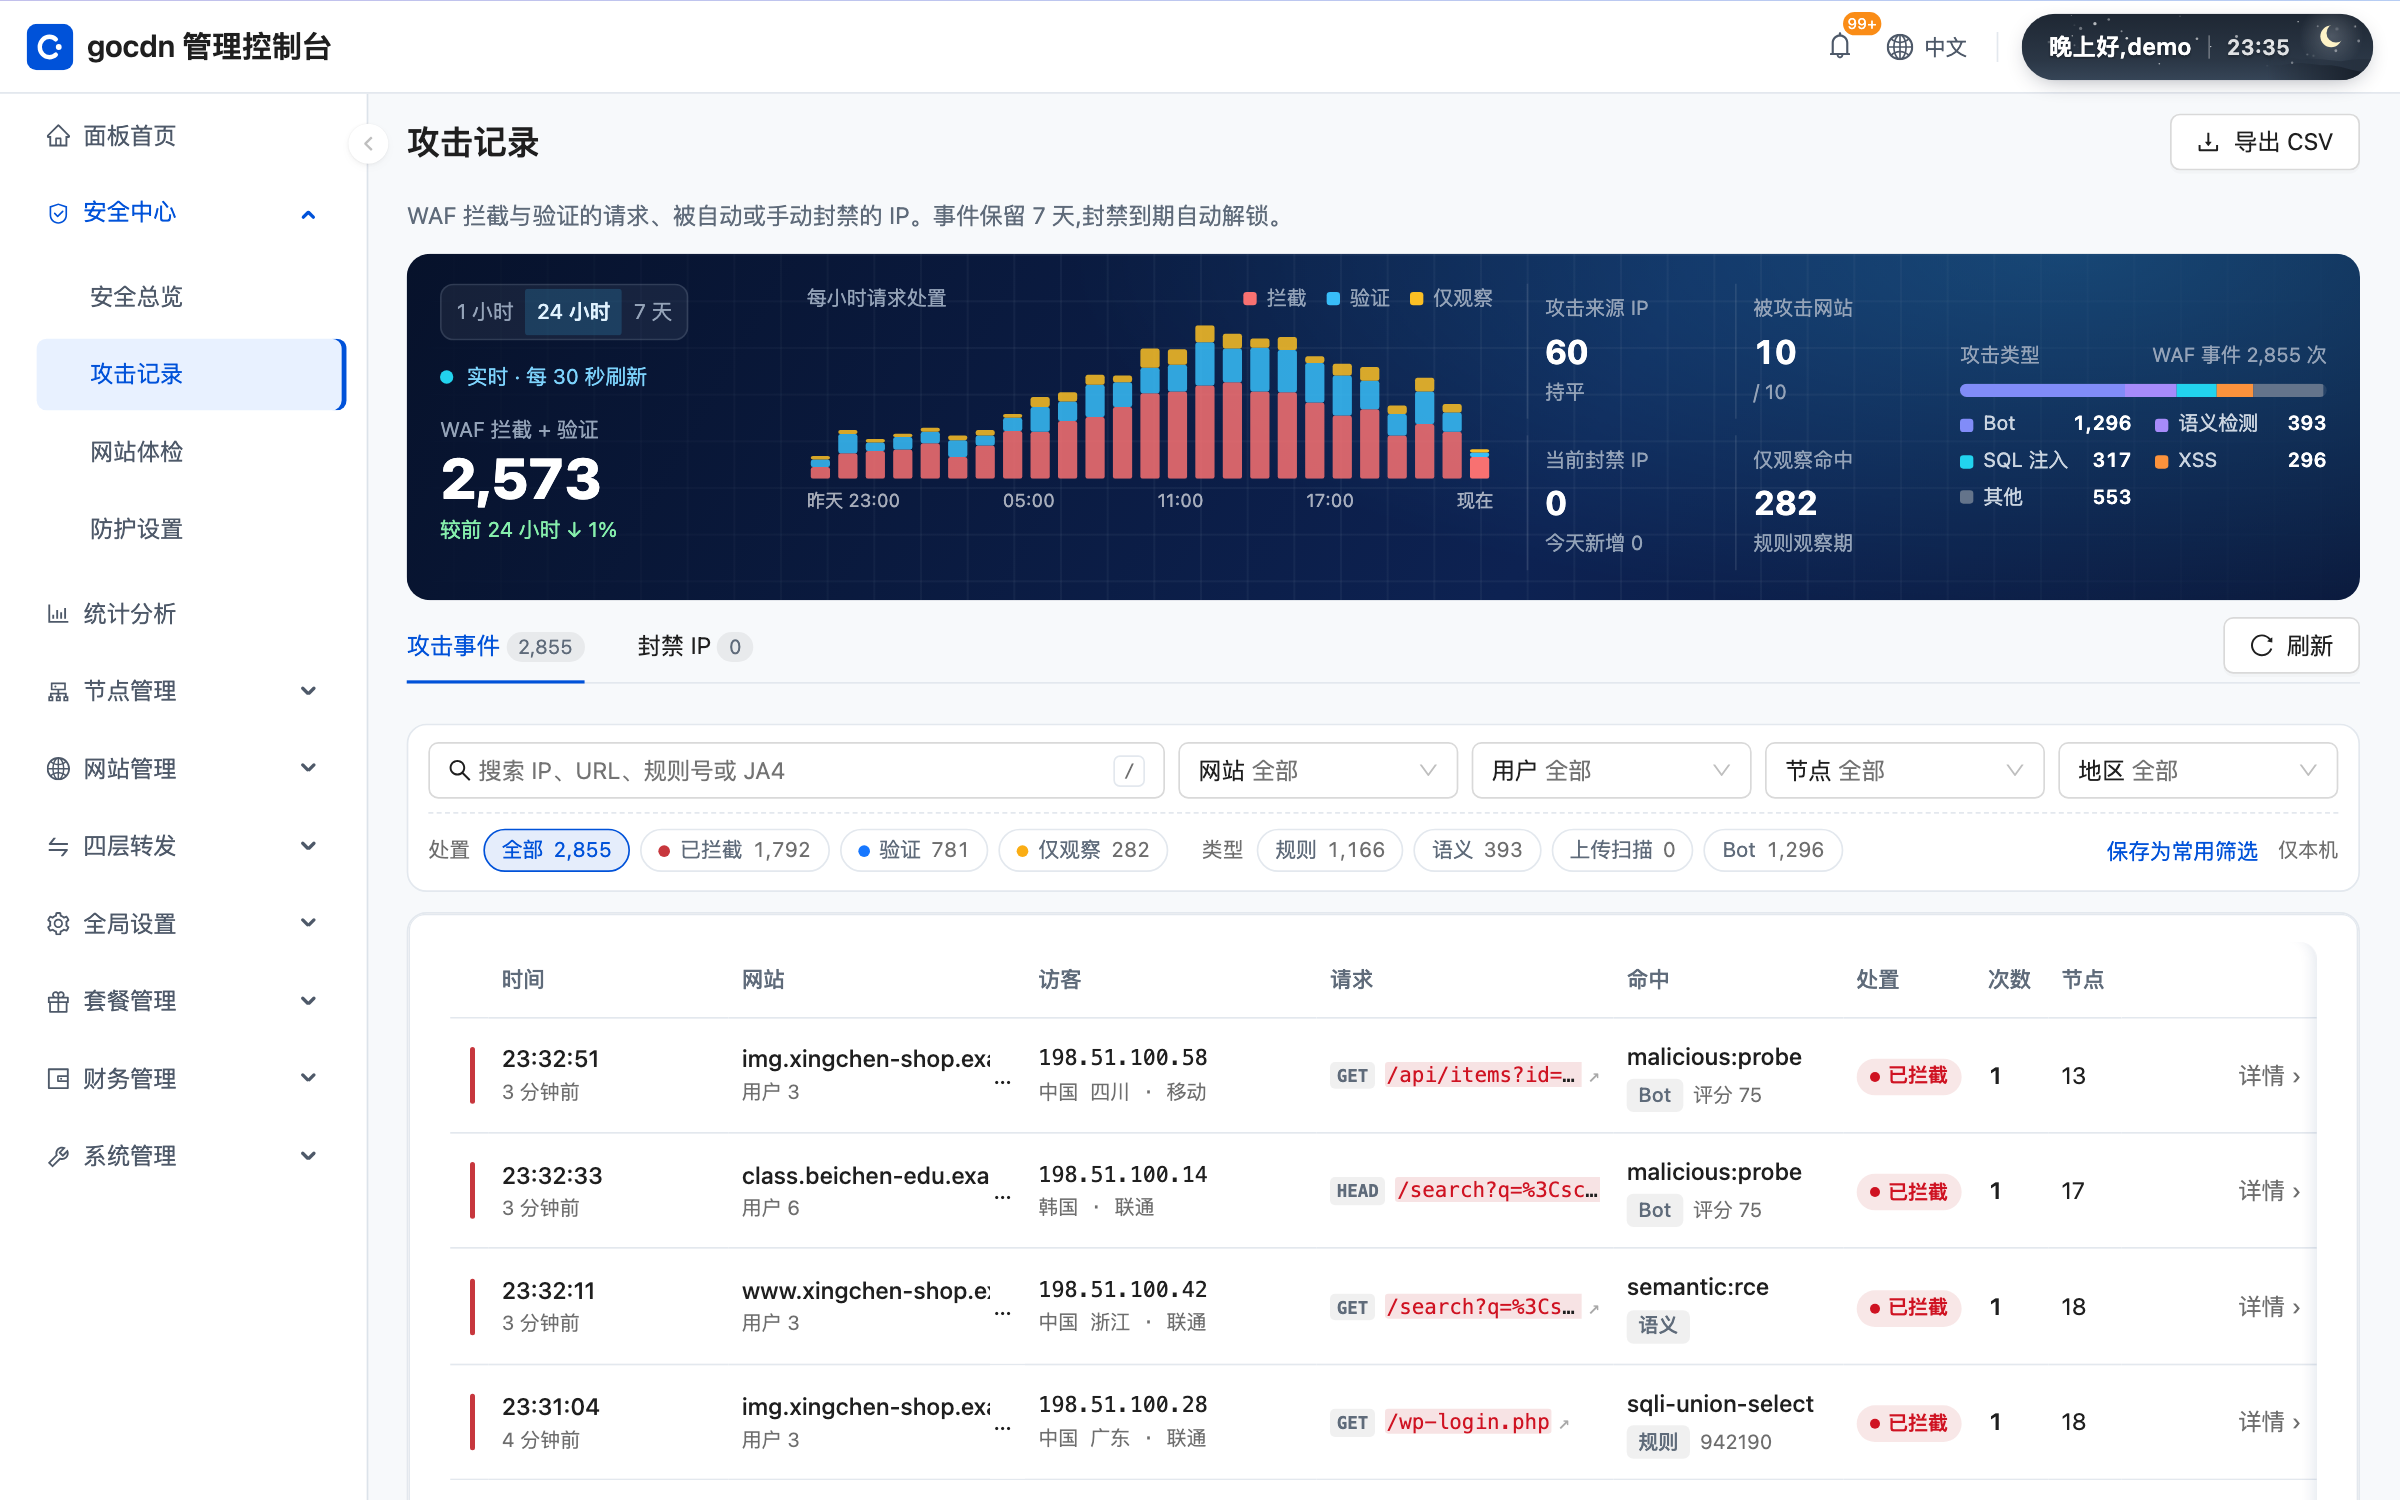
Attack Logs: fully traceable
Filter by time, IP, site, attack type or matched rule; see the request and where it matched; a source can be banned or allowlisted in one click.
- Events are kept for 7 days; bans lift automatically on expiry
- Attacks from the same IP are grouped together
- A false positive can be excepted in one click, without editing rules
Rule sources
Basic protection vs WAF Plus
Basic protection is included in every plan; WAF Plus is included by plan or available separately. Rules Update is priced separately; see the cards below
| Basic protection vs WAF Plus | Basic (every plan) | WAF Plus |
|---|---|---|
| Built-in rules for SQL injection, XSS, path traversal and more | Included | Included |
| CC protection, access control, auto-ban | Included | Included |
| Security Overview, Attack Logs | Included | Included |
| Standard / Strict protection levels | Not included | Included |
| Semantic detection (parses syntax, not just keywords) | Not included | Included |
| Advanced bot detection and behavior scoring | Not included | Included |
| Replay protection / page tamper protection / sensitive-data leak prevention | Not included | Included |
| Upload scanning: trojan signatures + virus library | Not included | Included |
| Security posture screen | Not included | Included |
WAF Plus
Deeper detection, fewer false positives
- Standard / Strict protection levels
- Semantic detection (SQL / HTML / JS parsing)
- Advanced bot detection and behavior scoring
Included in Enterprise and Unlimited
Security FAQ
How are legitimate visitors protected from false blocks?
New rules only log, without blocking, for their first 3 days. A false positive can be excepted in one click from Attack Logs, for that site and that rule only.
How do the basic rules differ from Rules Update?
Basic rules come with each release upgrade. With Rules Update, CRS converted rules, vulnerability patches, emergency rules and the high-risk IP library sync hourly, with no version upgrade needed.
How soon after disclosure is a new vulnerability covered?
Controllers with Rules Update sync every hour; others get coverage with the next release.
Is DDoS protection supported?
Application-layer (CC) attacks are covered. High-volume network-layer attacks depend on the protection capability of your data center and network.
Try the live demo
Open the live demo, or contact us for a quote and the install command